

Bank Security Access Control Systems: A Guide to Smarter and Safer Banking
- What Is a Bank Access Control System?
- The 4 Everyday Access Risks Every Bank Faces
- Key Features of a Modern Bank Access Control System
- How Access Control Secures Vaults, Cash Rooms, and Server Rooms
- Is Biometric Authentication Right for Banks?
- How Mobile Credentials Improve Bank Access
- How Banks Can Manage Daily Visitors
- How Access Control Integrates with CCTV, Alarms, and Identity Systems
- What Auditors and Regulators Expect in Bank Access Control
- Why Physical Access Control Is The First Line of Defense
- How Can a Bank Upgrade Access Control Without Rip and Replace?
Banks and financial institutions manage a unique kind of security risk. Protection of cash, sensitive customer records, and critical infrastructure depends on secure access, and a single access control gap can lead to theft, fraud, or unauthorized access to confidential information. Managing these risks becomes more complex across multiple branches, ATMs, and offices, where security teams need consistent control and visibility across every location.
Yet many financial institutions still rely on siloed access control systems, with permissions, security events, and audit records managed separately at each site. This makes it harder to track who enters restricted areas, revoke outdated credentials, and respond quickly to suspicious activity. IDCUBE Access360 brings access control, visitor management, and security intelligence together on one platform, helping banks strengthen physical security while maintaining control across their entire branch network.
This guide navigates you through the ins and outs of modern bank security access control.
What is a bank access control system?
Access control is a security system that decides who can enter a space, when they can enter, and how they prove who they are. Instead of relying on physical keys, it uses readers at the doors, controllers that approve or deny entry, credentials such as cards, mobile phones, or biometrics, and software that manages permissions and records every access attempt.
A bank security access control system applies these same building blocks to a bank’s environment, where the stakes are higher. It controls who can open which door, such as the vault, cash room, server room, or staff-only areas, and at what times. It also keeps a complete audit trail of every entry and denied attempt, which supports both day-to-day security and regulatory compliance.
The 4 everyday access risks every bank faces
Robust security starts with a basic question: “why” before “what” or “how”.
For physical access in banks, here are the four major risks.
- Lost or stolen credentials. A card proves that someone holds a card. It does not prove who that person is.
- Insiders with too much or outdated access. A loan officer who moved departments two years ago can still open the credit file room. A former employee’s access card was never revoked.
- Visitors. Auditors, consultants, contractors, and vendors need to get in, but only to specific areas and only for a set time.
- Disconnected sites. Branches and remote ATM sites depend on a network connection to check each credential against the central system. When that link drops, the door controllers at these sites can no longer verify who is allowed in. If the system isn’t built to keep working offline, those doors either stay locked for everyone, including authorized staff, or open for anyone, leaving the site unprotected
The core principle is that the level of access should match the level of risk. A branch lobby needs fast, easy entry. A currency vault needs strict, verified entry. Each area of a bank carries a different level of risk, so each needs its own access policy.
How bank access control has evolved
Most banks have moved through many generations of access control, and many branches still run a mix of them.
| Comparison | Mechanical keys | Standalone keycard doors | Networked, centrally managed system |
| Banking identity verification | Whoever holds the key | Whoever holds the card | Card, phone, biometric, or a combination, chosen per area |
| Removing a leaver’s access | Change the locks or hope the key comes back | Visit each door controller, or trust the card was returned | One change in a central console, applied across all sites |
| View across branches | None | Per door or per site | One dashboard for all locations |
| Evidence for auditors | Paper key logs | Partial, local logs | Time-stamped records of every attempt, searchable centrally |
| Main weakness | Cannot be audited | Separate systems that become out of date | Depends on good policy, integration and monitoring |
Key features of a modern bank access control system
Role-based access control (RBAC)
Role-based access control gives entry based on a person’s job role instead of a hand-built list of doors. A loan officer’s role opens the credit file room. A vault custodian’s role opens the cash loading room. When someone changes roles, their access changes with it, so old permissions do not pile up. Rules can also add branch, shift, department, and security level on top of role.
Multi-factor authentication (MFA)
Multi-factor authentication (MFA) at the door asks for more than one proof of identity. What does this mean in practice? Presenting a card plus a face match, or a mobile credential plus a PIN. It is deployed to restrict high-risk or high-value physical environments, for example, data centers and server rooms.
Dual custody and door interlocking
Dual custody (aka the two-person rule) requires two authorized people to present credentials within a set time. It can be used in high-security environments, for example, a vault or currency chest. Door interlocking keeps one door in a pair locked until the other has closed. Anti-passback stops one credential from being used to let a second person in.
Audit trails and real-Time monitoring
The consequences are not always immediate. So we need to keep an immutable, time-stamped record for every access event’s details. It consists of the details of the access, whether granted or denied, the name of the person, the time of access, and which area has been accessed. Records are most useful when they trigger alerts: repeated forced-door events, a door held open too long, or a controller that keeps going offline.
Applying zero trust to physical access
Zero trust is a buzzword in the BFSI industry. It is usually discussed for networks and applications, but the idea works for buildings too. In the zero trust architecture, no one is trusted just because they are already inside. Each sensitive door is checked again, access is limited to what the role needs, and unusual activity raises a flag. Entering through the lobby should never mean someone can walk into the server room.
How access control secures vaults, cash rooms, and server rooms
The practical method is to sort every area into a risk level and assign controls to each level.
Use the table below as a starting point and adjust it to your own risk assessment.
| Area | Main risk | Suggested controls | Level of checking |
| Lobby and customer areas | Unorganized, Difficulty handling in peak hours, after-hours entry | Time-based rules, intrusion alarm integration, video | Low |
| Teller line and back office | Unauthorized staff or visitors | Role-based access, card or mobile credential | Low to medium |
| Records and credit file rooms | Exposure of customer data | Role-based access, detailed logging, visitor escort rules | Medium |
| Cash room and ATM loading | Theft, collusion | Credential plus biometric, shift-based rules, alarms | High |
| Vault | Theft, coercion, collusion | Dual custody, biometrics, interlocks, lockdown capability | Highest |
| Server room and data center | Tampering, data theft | Multi-factor authentication, short approval windows, review of every entry | High |
IDCUBE’s Access Master module (part of the Access360 platform), sets a separate policy for each of these areas by role, branch, and shift. It supports two-person rules, multi-door interlocking, biometrics, and automatic lockdown and evacuation for vaults and server rooms.
Is biometric authentication right for banks?
Yes, biometric authentication in banking works well in banks, with some limits. Biometrics stop credential sharing, but they do not solve every problem. Here we mean employee identity checks using fingerprint, face, or vein recognition, both at physical doors and for recording attendance.
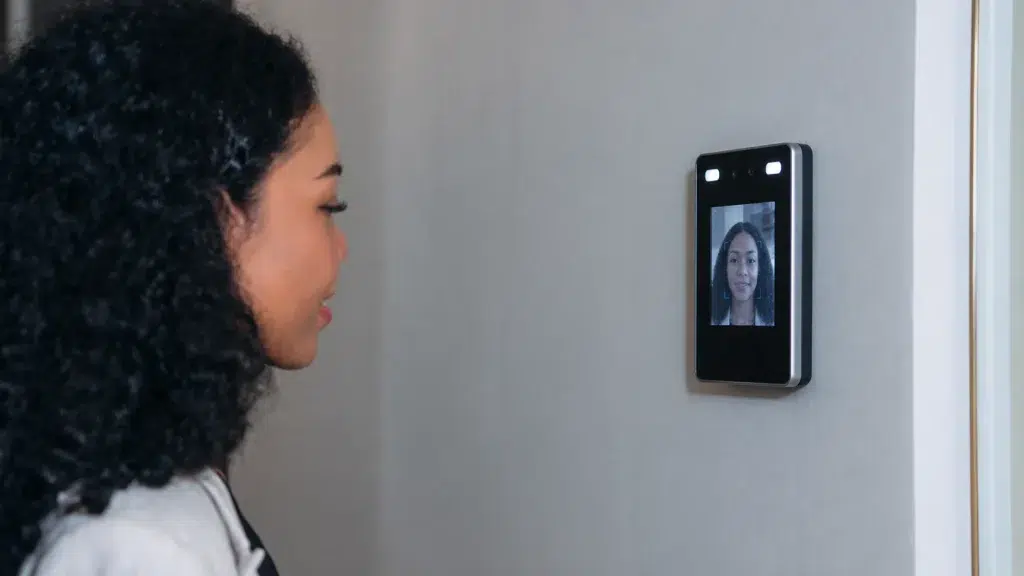
Pros: A face or fingerprint cannot be handed to a coworker. For example, a cash officer entering the currency counting room presents a card and a face match. If the card is lost or stolen, the face check stops anyone else from using it.
Cons: With that said, biometrics in banking need reliable enrollment, anti-spoofing, privacy safeguards, and secure backup access methods.
Pro-tip: Only use them for high-risk areas like vaults and server rooms. For lower-risk areas, access cards is enough.
How mobile credentials improve bank access
A mobile credential is a digital key stored on a smartphone and shown to a reader over NFC, Bluetooth Low Energy (BLE), or a dynamic QR code. For banks, the main benefit is access control. Credentials can be issued on an employee’s first day and revoked from a central dashboard the moment someone leaves. There is no plastic card to lose or forget to collect.
IDCUBE GreenID is an all-in-one app that could benefit in this scenario. It is a unified mobile access control app that offers convenient and secure mobile-based access; it can be used to manage visitors, for example, issuing digital passes. Its Control Center feature enables one-click emergency lockdown and evacuation across a branch or the entire bank network.
How banks can manage daily visitors
Banks involve visitors in the form of auditors, vendors, and technicians as part of their day-to-day operation. Visitors are a common blind spot if their access is not managed well. What works is pre-approval plus limited, time-bound access: the host registers the visitor in advance, the visitor verifies at reception, the pass works only for the approved area and time, and access ends automatically at check-out.
IDCUBE’s ezvisit10 follows this flow. It simplifies and secures visitor management across diverse facilities through ten adaptable workflows. There could be multiple access scenarios: host-initiated, visitor-initiated, and direct walk-in. Overall, it ensures an inclusive, seamless experience for all visitors and vendors by offering flexible access options like QR-based digital passes, self-service check-in kiosks, and desktop registration for high-security sites.
How access control integrates with CCTV, alarms, and identity systems
Access control becomes far more useful when it works with the security ecosystems around it.
- Video surveillance. Linking door events to camera footage turns a log line (“Door 14, 02:13, denied”) into evidence of who was there.
- Alarms and intrusion systems. Forced-door and held-open events should raise alarms, and alarms should be able to trigger a lockdown.
- HR and identity systems. Connecting HRMS, Active Directory, and Azure AD creates, changes, and removes access automatically as people join, move, and leave. This is the most effective fix for outdated access.
- Elevators. Linking floor permissions to access rights keeps employees on the floors their role needs.
Open vs. proprietary access control architecture
An open architecture system works with hardware and software from many vendors. A proprietary system ties you to one vendor’s readers and controllers. For a bank with a mix of older and newer branches, this choice decides whether an upgrade means replacing everything.
Access360 integrates with leading hardware platforms such as HID, Mercury, Idemia, Invixium, and Suprema, so banks can keep their existing readers and controllers. Confirm your exact models during the site survey.
For the link between reader and controller, look for Open Supervised Device Protocol (OSDP) with Secure Channel, which encrypts the communication. Older Wiegand wiring has no such protection. IDCUBE supports Aero and Mercury controllers with OSDP Secure Channel, TLS 1.3, secure boot, and FIPS 140-3 cryptography.
Cloud vs. self-hosted access control for banks
The main difference between cloud and self-hosted access control is who manages the infrastructure. With a cloud deployment, the service provider manages hosting and platform maintenance. With a self-hosted deployment, the bank runs the system on its own infrastructure or private cloud. A hybrid approach is also possible, combining cloud-based management with selected systems or infrastructure maintained by the bank, depending on the solution’s capabilities and integration requirements.
IDCUBE Access360 Core supports both SaaS and self-hosted deployment options, helping banks choose an approach that aligns with their IT infrastructure, security policies, and operational needs.
What auditors and regulators expect in bank access control
No access control product makes a bank compliant on its own. Compliance belongs to the bank’s security program. What the system provides is proof that the program is working.
Auditors typically look for:
- Documented access policies for sensitive areas.
- Clear records of who has access and why.
- Timely access revocation when roles change, or employees leave.
- Time-stamped access logs retained for the required period.
- Centralized visitor and contractor records.
- Evidence of regular access log reviews.
Certifications and compliance banks should check in an access control vendor
When banks evaluate an access control vendor, they need to look beyond the product itself. The vendor’s security practices, data protection measures, and testing processes also matter.
| Certification or assessment | Why it matters to banks |
| SOC 2 Type II | Provides independent assurance about the hosted service’s security and availability over time, particularly for banks considering SaaS deployment. |
| ISO 27001 | Demonstrates a structured information security management system, supporting third-party risk assessments. |
| ISO 27018 | Addresses the protection of personal data in cloud environments, including staff identities and access records. |
| GDPR | Supports data protection obligations for banks handling employee and visitor data under applicable GDPR requirements. |
| VAPT | Helps identify security vulnerabilities through assessment and penetration testing. |
| ISO 9001 | Demonstrates a quality management approach that supports consistent product delivery, installation, and support across branches. |
Note: IDCUBE Access360 Core aligns with all of the above certifications and compliance requirements.
Pro-tip: Ask for the current certificates and their scope as part of your vendor review.
Why physical access control is the first line of defense
IBM’s Cost of a Data Breach Report 2025 put the average breach in the financial sector at $5.56 million, compared with a global average of $4.44 million.
This figure covers all types of data breaches, not just physical ones.
But many digital attacks need a physical step first: plugging a device into a server, opening a records cabinet, or using an unlocked workstation in a back office. And physical access control stops that step in the first place by keeping unauthorized people restricted to the sensitive areas.
How AI analytics strengthen bank security
A bank generates a huge number of door access events, alarms, and records every day. This is practically not possible for a team to keep an eye on all of them. Analytics sum it up with the best representation: credentials unused for months, active credentials of former staff, repeated attempts at a restricted door, or controllers that keep going offline.
IDCUBE AInsights is the analytics layer of Access360. It converts all this access data into actionable intelligence and provides a vulnerability score for your facility. On top of that, you can ask about any security incident in plain English, which makes finding even months-old data super easy.
How can a bank upgrade access control without rip and replace?
There could be multiple scenarios to keep in mind while designing PACS in BFSI. Most BFSI institutions rely on legacy readers, controllers, and software spread across branches, along with plans to expand to new locations. Replacing everything at once is costly and disruptive, so the better approach is a phased upgrade built on an open-architecture platform, one that supports existing compatible hardware and industry-standard protocols such as OSDP.
Here is how it works in practice:
- Audit what you have. List every reader, controller, and credential type across all branches, and identify which devices are compatible with the new platform and which are outdated or unsupported.
- Upgrade the management software first. Move to a centralized, open-architecture platform that can run existing compatible readers and controllers, so the hardware stays in service while the bank gains central control and reporting.
- Secure high-risk areas next. Prioritize vaults, cash rooms, and server rooms for new hardware, multi-factor authentication, and biometrics, since these carry the most risk.
- Integrate employee identity systems. Connect the platform to HR or identity management so access is granted on joining, updated on role changes, and revoked automatically on exit.
- Pilot at one branch. Test the full setup at a single site, fix issues, and refine policies before rolling it out network-wide.
- Replace outdated hardware gradually. Swap legacy devices branch by branch, in line with budgets and maintenance cycles, rather than all at once.
Conclusion: building a smarter, safer banking environment
Banks and financial institutions operate in a highly regulated environment. As most banks still rely on legacy access control systems, this risk becomes high. With multiple branches, security risks are not confined to one location, and a single loophole can have an impact across the region. Outdated access systems, excessive permissions, and gaps in monitoring can expose cash, customer data, and critical infrastructure. A modern access control system helps banks strengthen security, improve audit readiness, and maintain consistent control across locations.
A platform like IDCUBE Access360 brings access control, visitor management, and security analytics together on one platform, helping financial institutions manage access risks more effectively.
FAQs
How much does a bank access control system cost?
There is not a one size fit all solutions. Cost depends on the number of doors and branches, the credential types (cards, mobile, or biometric technology in banking), and the deployment model. Reusing existing readers and controllers lowers the upfront cost, and a SaaS deployment turns server costs into a predictable subscription.
Can we keep our existing card readers and controllers?
Yes, look for an open-architecture access control solution that allows integration with the existing hardware at your locations. This lets you upgrade the software first and replace hardware gradually, without disrupting daily operations.
IDCUBE Access360 Core is one such platform. It works with hardware from leading manufacturers like HID, Mercury, Idemia, Invixium, Suprema, and others, so banks can keep compatible devices in service while moving to centralized management.
How long does it take to roll out access control across branches?
Most banks start with a pilot at one branch and one data room, then roll out in phases. A pilot can typically run in a few weeks, while a full multi-branch rollout is planned over several months depending on the number of sites.
Is cloud-based access control safe for banks?
Yes, it is safe when paired with a multi-layered security strategy, strict compliance controls, and strong encryption.
How does anti-passback work?
Anti-passback stops one credential from being used to let a second person in. Once a credential has entered an area, it cannot be used to enter again until it has exited. It needs readers on both sides of the door to work well.